
One vault for every kind of credential.
Store logins, SSH keys, API keys, environment files and secure notes in a vault organized by type — envelope-encrypted, with no plaintext credential material at rest, and built for how engineers actually work.
the problem
Credentials sprawl across password managers, .env files, shared docs and chat. Nobody knows what is still valid, who can see it, or when it was last rotated.
What it does
- Typed, structured credentials
- Logins, SSH keys, API keys, env files, payment cards, identities and secure notes each get a purpose-built form — not one generic note field.
- Import without a clean slate
- Bring your history from 1Password, Bitwarden and Dashlane, plus SSH client configs, so adoption isn't a rewrite-everything project.
- Rotation and expiry
- Track expiry, flag weak or reused passwords, and rotate in place so stale credentials don't linger.
- Sharing that expires
- Hand off a credential with an encrypted, revocable, time-boxed link instead of a plaintext paste — and see when it was opened.
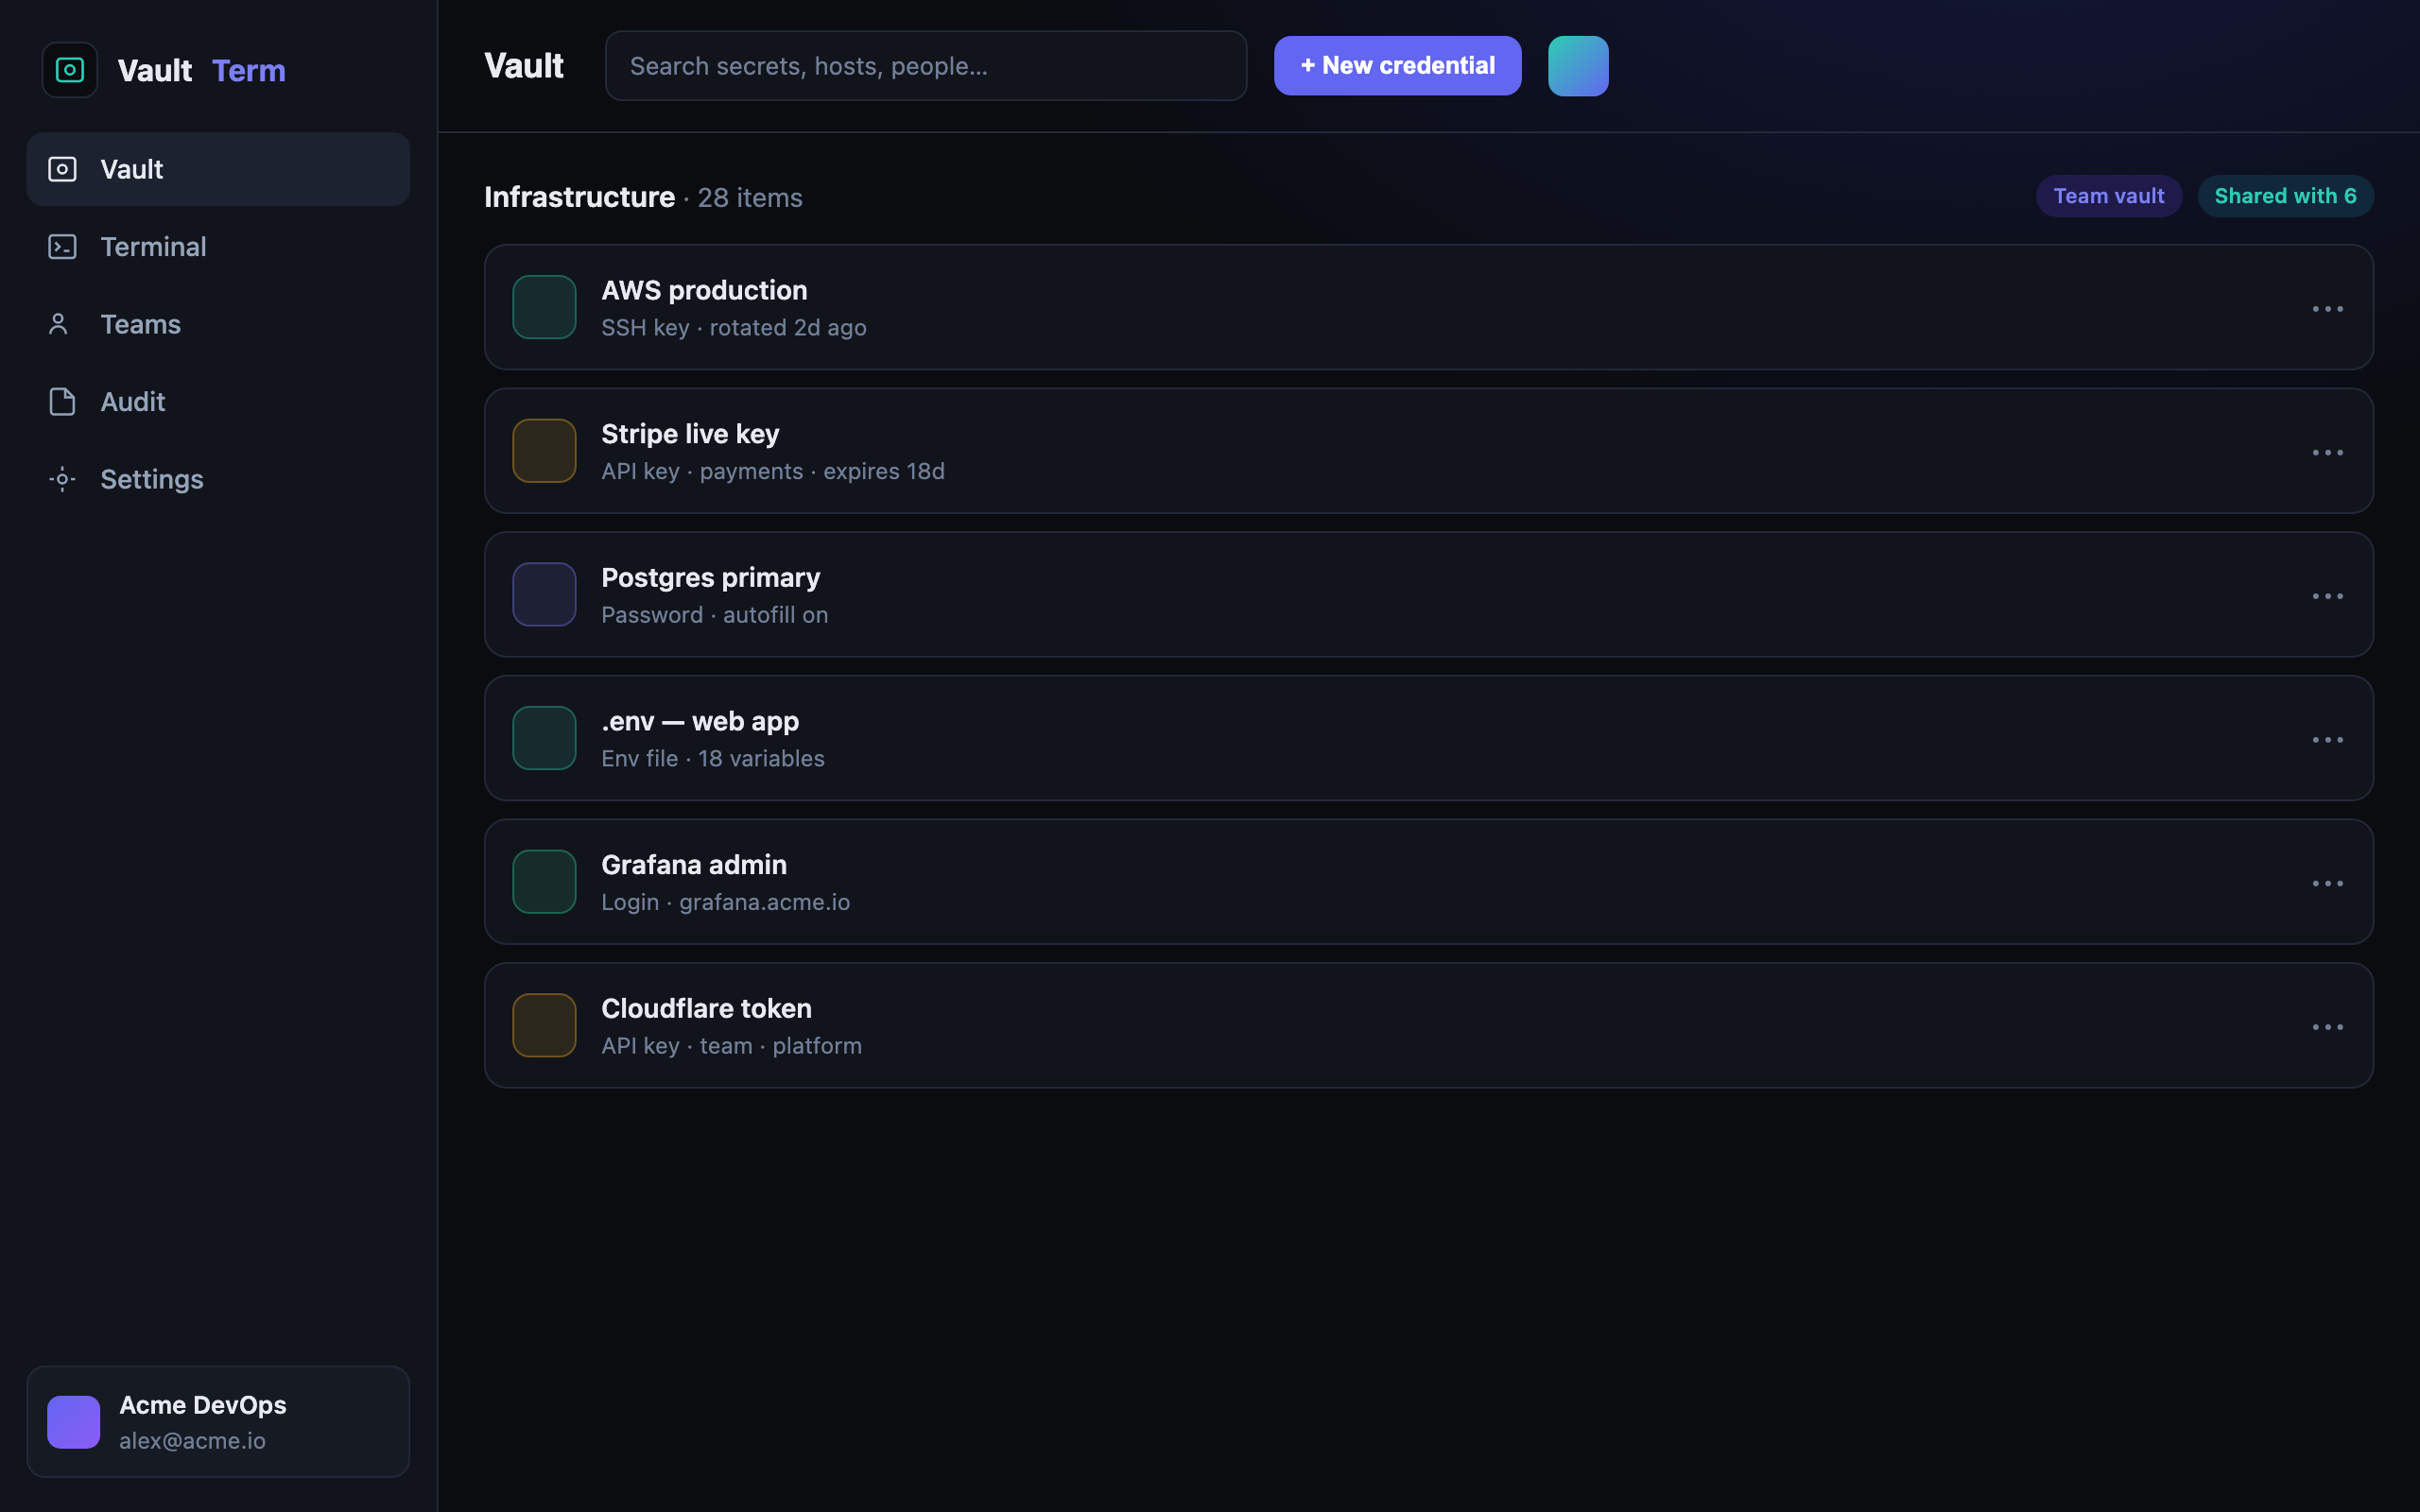
- Per-type forms for logins, keys, env files and notes
- Import from 1Password, Bitwarden, Dashlane and SSH clients
- Expiry tracking and one-click rotation
- Autofill config and secure sharing
how we back it up
No hand-waving on security
faq --list
Vault — questions
How is my vault protected?
Every credential is sealed with envelope encryption and there is no plaintext credential material at rest. The server decrypts a credential in memory only for an authorized, audited action, and that read is written to a tamper-evident trail. The security page states the full model.
Can I import from my current password manager?
Yes — 1Password, Bitwarden and Dashlane exports import directly, along with SSH client configurations, so you can move without starting over.
What kinds of credentials can it store?
Logins, SSH keys, API keys, environment files, payment cards, identities, TOTP seeds and free-form secure notes — each with a form suited to its type.